StiltaSecurity

Security for
confidential patent work

Visit trust center
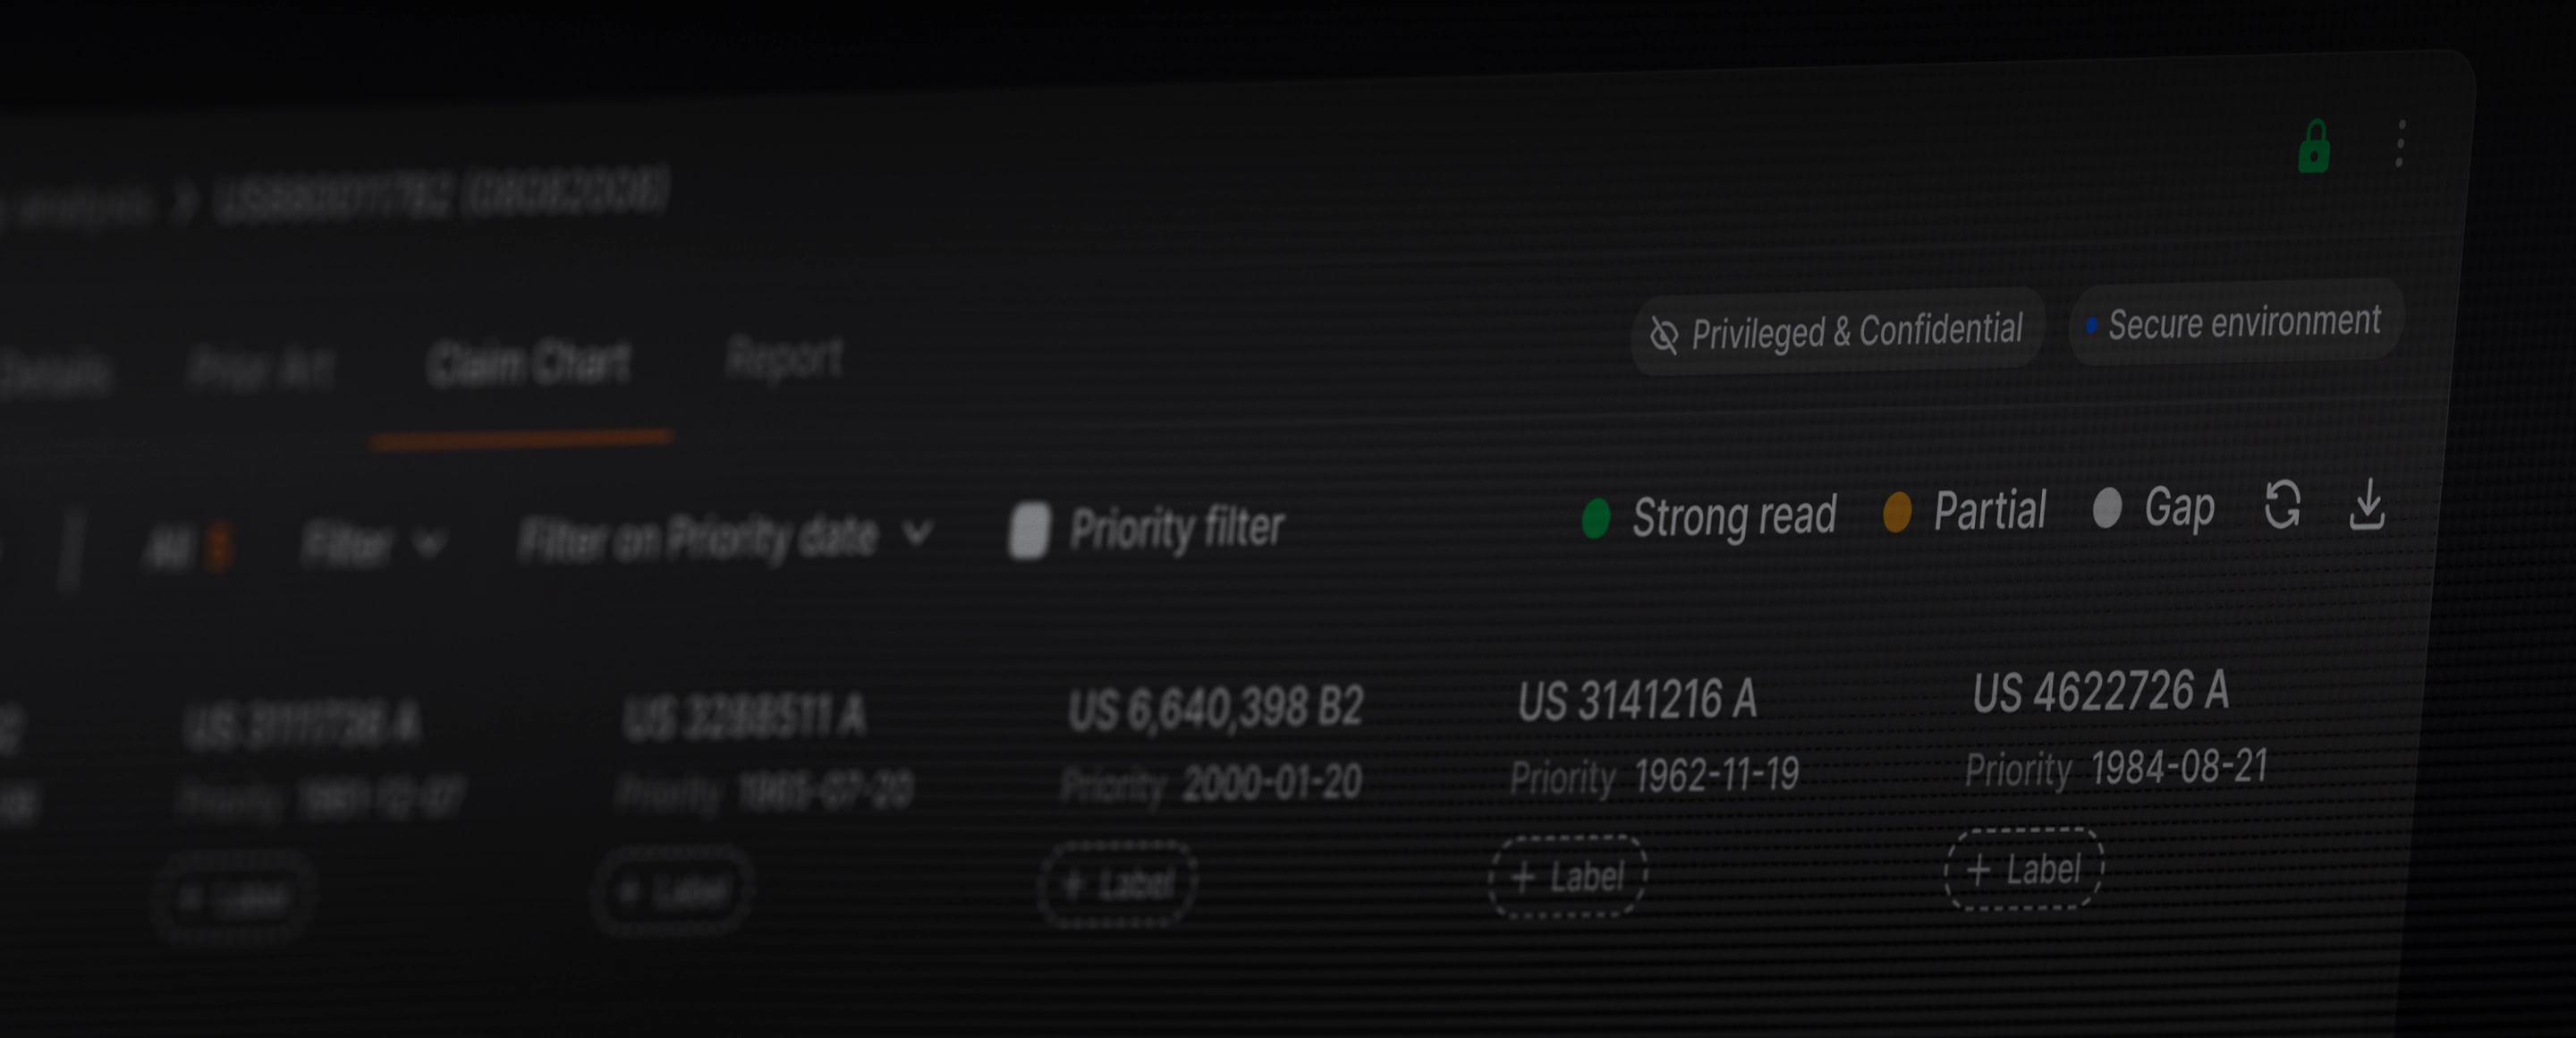
Stilta claim chart workspace marked Privileged & Confidential and running in a secure environment.
StiltaSecurity

Enterprise-grade security

Patent work routinely involves unpublished inventions, deal-sensitive product plans, and client secrets. Stilta is built by engineers who deployed AI in security-reviewed enterprise environments at McKinsey and QuantumBlack. We brought that same bar into Stilta from day one.

That means zero AI training on your data, per-tenant isolation by default, privileged work product never leaving your team, and your choice of US or EU data residency. Every model provider we work with is bound by separate confidentiality terms, so your unpublished inventions never enter someone else's training corpus. Standard enterprise controls - SAML SSO, audit logs, encryption at rest and in transit, regular penetration testing - are built in by default.

Confidentiality at every step

No training on your data

Your documents, prompts, and results are never used for AI training, fine-tuning, or model evaluation. This commitment binds Stilta and every model provider we use, under contract.

Private projects, shared on your terms

Your projects are private to you by default. You choose which projects to share. Your organization’s data stays isolated from other customers’ data.

Access only with your approval

Stilta staff can access your content only with your explicit written approval.

Encryption in storage and transit

Your data is encrypted in transit using TLS 1.2 or higher, and encrypted at rest through Azure’s key management or BYOK

Enterprise access controls

Connect your identity provider through SAML or OIDC single sign-on. Enforce multi-factor authentication and let administrators export audit logs for review.

Control over your data

EU or US data residency

Choose the EU or US for data storage and AI processing. Your selected region covers both where your content stays and where AI processes it.

Zero retention by model providers

Our model providers process your content to return a response, then retain none of it. This applies to your documents, prompts, and results.

Export and deletion

Request an export or deletion of your data at any time. If you leave Stilta, we delete all your data within 30 days.

Everything you need for your security review

Visit our trust center to review our SOC 2 Type II report, ISO 27001 certificate, penetration test documentation, data processing agreement, and subprocessor list.

Visit trust center

SOC 2 Type II

Independently tested through a SOC 2 Type II audit, monthly external penetration tests, and continuous code and dependency scanning. Our internal controls and data security practices are built for the bar enterprise security teams expect.
GDPR

Privacy-first processing aligned to GDPR, with US or EU data residency on Microsoft Azure. EU customers are hosted in Sweden, with encrypted backups in a second EU region. US customers' data can be hosted in the United States.

ISO 27001

Our information security management system is aligned to ISO 27001. Your work is encrypted in transit with TLS 1.2 or higher and at rest through the cloud provider's key management, safeguarding every patent matter.

EU AI Act

Built to the EU AI Act standard for high-stakes legal work. Transparent reasoning, evidence-backed outputs, and human-in-the-loop by default.

FAQSecurity and privacy

Common questions.
Plain answers.

Choose the EU or US for data storage and AI processing. Your selected region covers both where your content stays and where AI processes it.

Bring a patent matter. Leave with a defensible answer.

Book a demo